Lifecycle resources
Follow Certificate and related issuer resources to understand status and configuration.
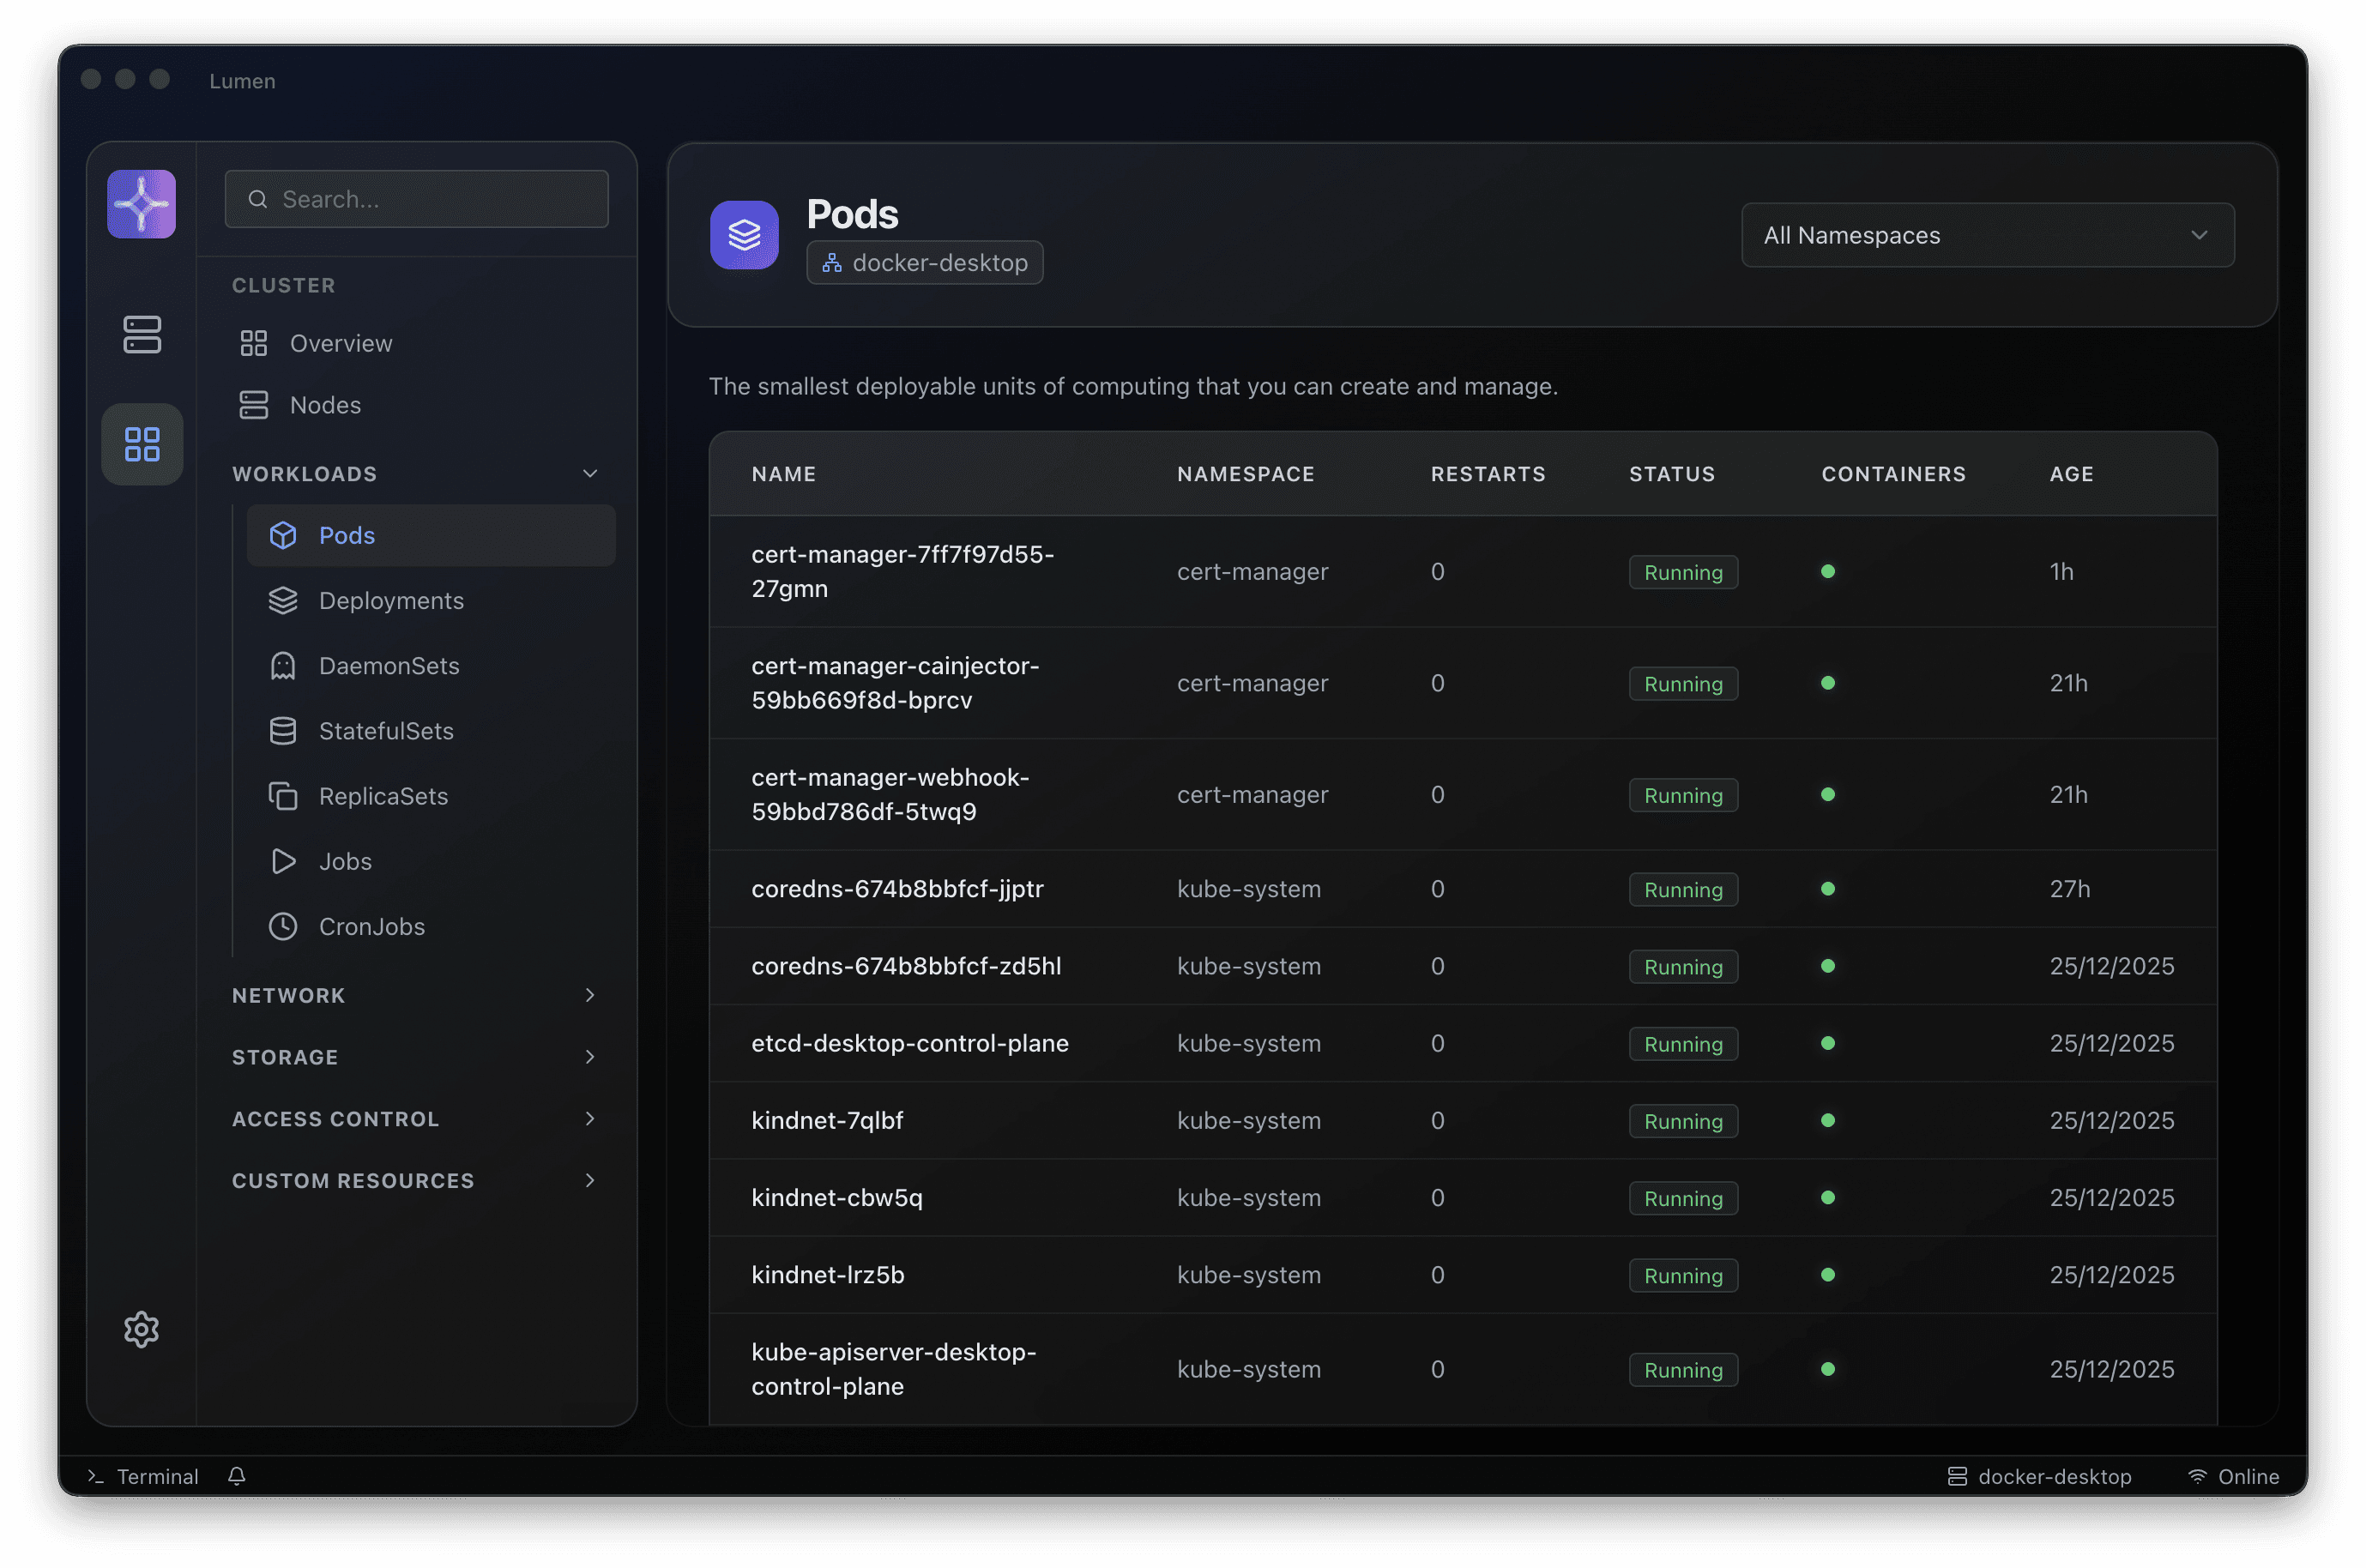
Lumen / cert-manager visibility
Certificates sit across resource relationships, issuer configuration and workload dependencies. Explore the Kubernetes objects behind TLS issues within your working cluster context.
01 / In your workflow
Follow Certificate and related issuer resources to understand status and configuration.
Look at associated resources and events when renewal or issuance needs attention.
Use credentials scoped to the resources you need. Treat certificate and Secret access as a separate permission decision.
02 / A considered investigation
cert-manager manages issuance and renewal. Views depend on installed resource versions and your Kubernetes permissions.
Start with your existing kubeconfig. Choose the cluster and namespace before investigating a resource.
Connect resource state with related workloads, events and logs. Build a picture of the issue before changing the system.
Inspect YAML and diffs, confirm the environment and permissions, then apply your team’s normal review and change process.
03 / Team adoption
Choose a representative non-production environment. Confirm resource visibility and credential boundaries, work through your common investigations and document the behaviours you want your team to standardise.
A clearer next step
Choose a release, connect an existing Kubernetes context and work through an investigation your team knows well. Talk to us when you need help with rollout or enterprise adoption.